




















































































Sophos published a detailed threat research from SophosLabs on Baldr, an information-stealer that first appeared January 2019. The report, Baldr vs the World, provides a deep dive on the popularity of the malware and its unique killchain characteristics. The in-depth research also reveals Baldr’s inner workings, including cybercriminal behaviors and missteps on both the selling and buying side that potentially led to its sudden disappearance from the deep web in June.
According to SophosLabs, the people who developed Baldr made it to sell to entry-level cybercriminals on the deep web and they, in turn, targeted PC gamers as the first set victims. Baldr has since gone way beyond infecting gamers and attacks have spread to encompass all computer users.
Baldr, like many types of malware, uses code fragments borrowed from other malware families. However, Baldr goes to further extremes and consists of copied code from a large number of other malware, making it more like a “Frankenstein’s monster of code snippets.”
One reason computer users should be aware of Baldr is because it can quickly ransack a wide range of information from its victims, including saved passwords, cached data, configuration files, cookies and other files, from a wide variety of applications.
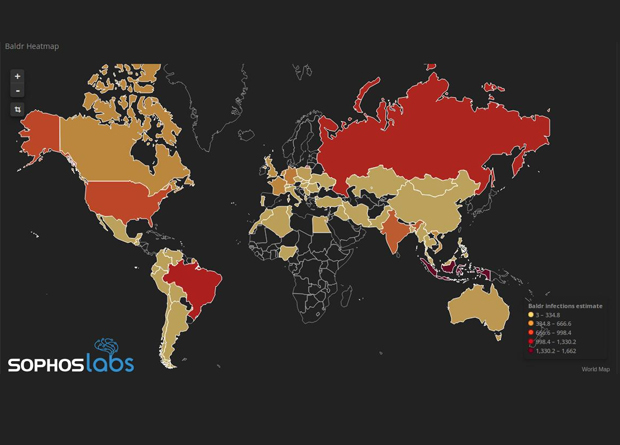
SophosLabs has tracked infections worldwide, including in these countries:
- Indonesia (more than 21% of the victim population)
- United States (10.52%)
- Brazil (14.14%)
- Russia (13.68%)
- India (8.77%)
Baldr heatmap from SophosLabs
Baldr disappeared from sale in June, apparently following an argument between the creator and the distributor. SophosLabs expects it to re-emerge in time, perhaps with a different name.
“Whether Baldr was a flash-in-the-pan that quickly peaked and then fell victim to a squabble among cyberthieves or will return as a long-term threat, remains to be seen. However, its very existence is a good reminder that even stolen bits of malware code stitched together to create a ‘Frankenstein-like malware monster’ can be incredibly effective at bursting in, grabbing everything and rushing out again. The only way to stop such threats is with basic, but essential security practices that include using up-to-date security software,” said Albert Zsigovits, a SophosLabs threat researcher in Hungary.
Gamers Beware
Gamers typically utilize much more powerful systems and are more willing to install custom tools, utilities, and applications from a wide variety of sources, all of which make them ideal targets for malware authors. Furthermore, utilities that enable “cheats” often use common malware techniques such as DLL injection, or modifying or injecting code into memory. This not only can lead to system instability, but also ruins the game experience for everyone involved.
“Even though Baldr is currently off the deep market, it can still be used by cybercriminals who had previously purchased it, and is still a potential threat. In general, PC gamers and all computer users should be wary of malware and take steps to protect their systems with security software like Sophos Home, which scans gaming software and cheats,” said Zsigovits.
How to Protect Against Baldr Malware
To protect against Baldr, computer users should be wary of phony online advertisements and videos promising “too much” – if it looks too good to be true, it probably is. Always use basic and best cybersecurity practices at all times on all devices. Businesses can use an enterprise security solution that detects malware, such as Sophos Intercept X, which also protects against ransomware. Sophos Home, is ideal for scanning gaming and family computers to detect Baldr and other malware.
Sophos Home deploys a layered security approach, combining behavioral detection, advanced exploit protection, anti-virus and AI based static detection that work in tandem to protect gamers. Additionally, Sophos Home protects file transfers from questionable gaming sites and servers by analyzing network traffic to detect malicious traffic and by scanning downloaded files in real time as they are written to the file system. Combined with protection from phishing sites and remote management features, Sophos Home provides a well-rounded approach to protection that is an ideal security choice for gamers.
Lastly, all computer users need to be smart about passwords. Use and change complex passwords frequently, use unique, one-of-a-kind passwords for banking and other financial online accounts and monitor accounts for suspicious activity.

























