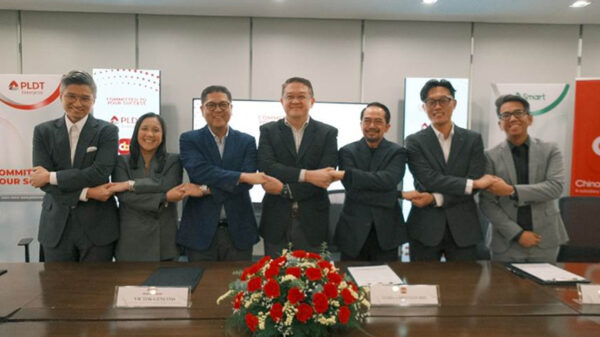
PLDT and its wireless unit, Smart Communications, Inc. (Smart) warn internet users that hackers are targeting employees to breach the cyber defenses of companies. Rather than directly take on security software in place, PLDT and Smart’s Cyber Security Operations Group (CSOG) says hackers will use unsuspecting employees to gain access to the companies’ network.
“Vigilance is key. Cybercriminals take advantage of the employee’s carelessness to steal his or her credentials which they will use to infiltrate the company’s digital assets. This is why it is important for organizations to adopt a culture of cybersecurity,” warned Angel T. Redoble, FVP and Chief Information Security Officer of the PLDT Group.
Quoting a report by Romanian cybersecurity technology company Bitdefender, CSOG says hackers will go after employees 99% of the time by employing social engineering to coax their victims into revealing their personal information. This could be executed through phishing emails, vishing or SMShing that mimic legitimate communication materials or messages from a known company.
PLDT and Smart share tips on how to protect yourself from these attacks.
- Interact only with people you know. Open trusted applications and websites. Remember, never open emails from strangers or click links from dubious senders.
- When prompted, update applications and operating systems installed in your devices to get the latest security patches that will address known vulnerabilities. But CSOG warns users to click legitimate alerts from their developer’s official platforms.
- To add another layer of protection, CSOG encourages users to enable Multi-Factor Authenticators. This feature also alerts users when dubious personalities are trying to access accounts from unknown devices or locations. Remember, never share your One-time Passwords or OTPs with anyone.
- Finally, CSOG suggests using strong and long passwords or a combination of special characters, upper and lowercase letters, and numbers. CSOG also reminds internet users to use different passwords for different accounts and to change them regularly.
If you receive a dubious or malicious message, take a screenshot, and send it to cybersecurityincidents@smart.com.ph. You can likewise report other cybersecurity matters like phishing, vishing, and malicious domains though this channel.
The efforts of PLDT and Smart to share CyberSmart tips on keeping customers safe online are fundamental to the PLDT Group’s much broader program to elevate the quality of customer experience by protecting them from threats and cyber-attacks.