








































































Connect with us

Hi, what are you looking for?

HEADLINES

LinkedIn opens about data breach; urges users to stay safe

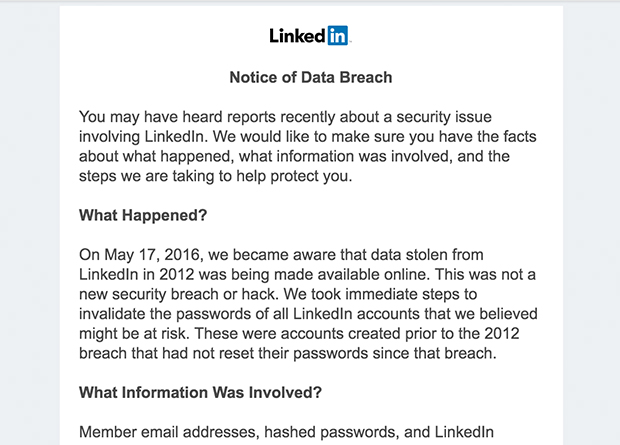
LinkedIn has emailed its members a notice on data breach, even as it reiterated that it is taking steps to help protect its members.
LinkedIn has emailed its members a notice on data breach, even as it reiterated that it is taking steps to help protect its members.

LinkedIn LinkedIn2

According to the email, LinkedIn became aware on May 17 that data stolen from LinkedIn in 2012 was being made available online. It emphasized that “this was not a new security breach or hack.”

Information involved in the breach include: member email addresses, hashed passwords, and LinkedIn member IDs (an internal identifier LinkedIn assigns to each member profile) from 2012.

Already, LinkedIn “took immediate steps to invalidate the passwords of all LinkedIn accounts that we believed might be at risk. These were accounts created prior to the 2012 breach that had not reset their passwords since that breach.” In addition, “we are using automated tools to attempt to identify and block any suspicious activity that might occur on LinkedIn accounts. We are also actively engaging with law enforcement authorities.”

However, even as LinkedIn itself is taking steps to strengthen security, “we always suggest that our members visit our Safety Center to learn about enabling two-step verification, and implementing strong passwords in order to keep their accounts as safe as possible. We recommend that you regularly change your LinkedIn password and if you use the same or similar passwords on other online services, we recommend you set new passwords on those accounts as well,” LinkedIn ended.


Advertisement. Scroll to continue reading.
Advertisement
Advertisement
Advertisement

Like Us On Facebook

You May Also Like

HEADLINES

Techniques include malicious email, phishing, compromised credentials and brute force attacks. The 85% rate exceeded the cross-sector average of 79%, underscoring the role identity...

HEADLINES

Sophos Counter Threat Unit (CTU) researchers observed an Exploit forum persona named Optimus_Prime advertising Luciferus on August 24, 2026.

HEADLINES

People need to know what kinds of concerns can be raised, where to bring them and what steps to take when something does not...

HEADLINES

Consider deploying a dedicated security solution that safeguards corporate emails from spam, email-borne infections, and all forms of phishing – such as Kaspersky Security...

HEADLINES

The attack begins with a malicious file ending up on a user’s device – this may be a result of the user downloading the...

ELECTRONICS

While most brands compete on how many passwords a lock can store or how much force a safe can survive, Philips built its ecosystem...

HEADLINES

The recognitions, provided by Frost & Sullivan, highlight Kaspersky’s ability to align its cybersecurity strategy with the evolving needs of industrial organizations while executing through...

HEADLINES

EastWest has introduced EasyLock, a self-service security feature available through the EasyWay and EasyBiz apps, where customers can secure a chosen portion of their balance,...

Advertisement























