




















































































As cyber threats targeting financial institutions become more sophisticated and coordinated, there is a need to beef up cyber security to fend off attacks in banks where the money is. This is according to Joey Regala, president of Information Security Officers Group (ISOG) and VP and head of IS Operations at United Coconut Planters Bank, during the ISOG Summit.
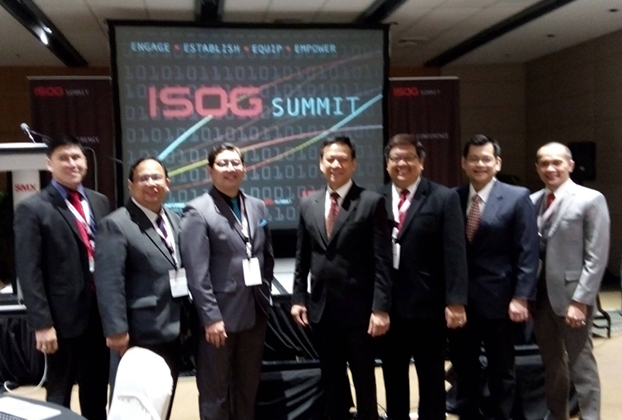
ISOG President Joey Regala (fourth from left) with other ISOG directors
“Your money is what we’re trying to protect from unauthorized access, disclosure, destruction, multiplication, inspection, recording and deduction,” said Regala, who discussed the current state of the financial industry and how information security officers (ISOs) protect banks and the money in it.
Regala said they, as security officers, focus on minimizing risk by implementing and maintaining a defense mechanism across network infrastructure to secure users’ information, systems, networks as well as money.
“Currently, we’re using the defense in-depth security strategy. We defend your money through a series of different levels of defenses such as fiscal layers, network layers, application layers, and so on and so forth,” said Regala.
They use different levels of defenses so that in case one defense fails, there are others that can still secure the money in banks.
However, since they have been using this strategy for quite sometime, Regala stressed that as information security officers, “we believe we need to upgrade our defense.”
The signature-based detection is another strategy to protect banks. Regala said this instrument is based on a certain footprint or signature of a file and in case there is no signature, it can compromise the system.
Aside from these defense strategies that secure operations of banks, Regala admits that the banking industry needs to upgrade competencies of its people in order to meet the requirements of the industry especially now that hackers are more intelligent and threats are more sophisticated.
“Admittedly, we have lack of skills but we have skilled people. We do need to upgrade our competencies,” said Regala. “People in the banking industry are competent but as the hacking or as the vulnerability increases, the competency should be parallel or we should align with the needs. That’s what we are seeking.”
Regala said they can solve this by engaging people to promote a web of trust in the finance industry; by establishing the right standard and equipping people not only with right competencies but also with tools, equipment, firewalls, and so on; and by collaborating with anti-cybercrime groups.
With the rise in sophisticated threats, Regala disclosed that the new breed of hackers has information asset as its new denomination. These assets consist of identity data – card number, account number, ATM number, information of a person and credentials.
“They don’t steal money but they can steal something that can be used as an instrument to get the money,” said Regala. “As people update security, hackers will also upgrade their attacks. They are impatient and they are no longer hooded.”
Because of this new breed of hackers, Regala is warning people to be more vigilant, more conscious and be aware of the threat.
“You should be aware because you are the endpoint, you are the victim. You are the weakest link to our security chain and this is the new concern of information security,” said Regala. “Before, we just defend. Now, the advance way of defending your turf is going beyond. We’ll be using more sophisticated tools and process all activities through their behavior. This is now the culture of information security.”




























